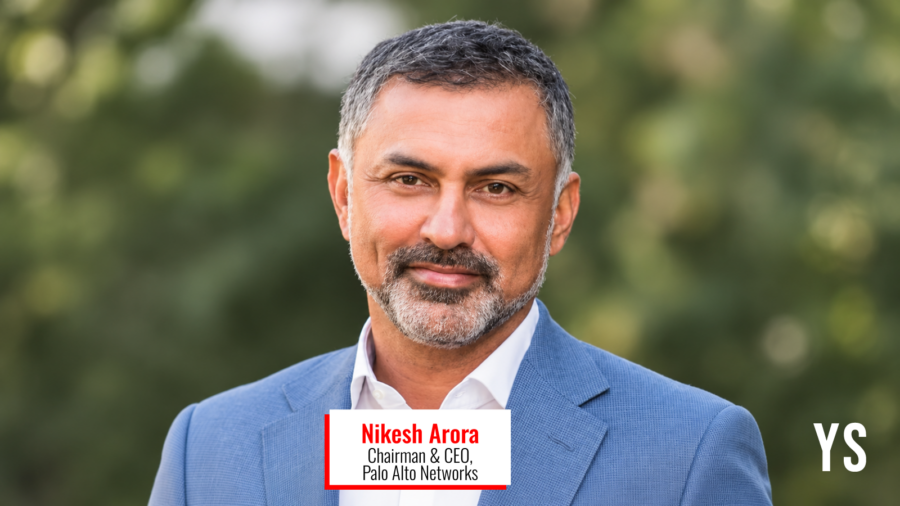
Artificial intelligence is identifying software vulnerabilities faster than most organizations can resolve them, according to Palo Alto Networks CEO Nikesh Arora. While AI tools improve cybersecurity defenses, they simultaneously provide attackers with rapid methods to exploit enterprise system weaknesses.
Key Cybersecurity Challenges
- Patching speed concerns: Organizations, particularly smaller firms, lack the capacity to fix vulnerabilities at the rate AI discovers them.
- Verification hurdles: Security teams must confirm flaws, assess risks, and test fixes against existing applications to avoid service disruptions.
- Rising vulnerability volume: The U.S. National Institute of Standards and Technology reported a 263% increase in National Vulnerability Database submissions between 2020 and 2025.
- AI-driven defense initiatives: Tech firms like Anthropic and OpenAI are experimenting with AI to generate candidate patches and identify high-severity flaws.
- Virtual patching recommendation: Industry experts suggest virtual patching as an interim measure to block exploitation attempts without altering underlying software.
The Gap Between Detection and Remediation
Arora noted that finding a flaw is merely the initial step in a complex lifecycle. Teams must validate the finding, prioritize the risk, and deploy a fix. He cautioned that relying on a single model is insufficient, as different AI models identify distinct weaknesses. Furthermore, false positives waste valuable time, while untested patches risk operational disruption.
Data from the U.S. National Institute of Standards and Technology underscores the growing scale of the problem. Despite enriching nearly 42,000 records in 2025, the agency struggled to keep pace, eventually adopting risk-based prioritization in April 2026 to focus on critical software threats.